Download the Full PDF
Strengthening security posture at a leading Belgian insurer.
With cybersecurity becoming critical, Fédérale Assurance set one clear priority: control over employee access to the critical parts of its IT infrastructure. The CISO wanted a fast approach that avoids large, risky up-front investments and puts real security improvements first. They chose Elimity to get provable control through lightweight, data-driven identity governance.
800 employees · 200 entitlements · 250 roles · 8 identity sources
Elimity Insights is a simple solution that allows you to collect information and slice and dice it across many sources of information. I have never encountered another tool that can provide you with that many insights in just three to four days.— Luc Castan
“When facing this kind of challenge, organisations traditionally have two options: they either implement a full stack identity governance solution, or they make an inventory of access rights by interviewing people and filling out spreadsheets. We wanted a third option.”— CISO, Fédérale Assurance
The two classic options were a full identity governance suite or a manual inventory based on interviews and spreadsheets. Fédérale Assurance chose a third way: lightweight, data-driven visibility on their own identity data.
Challenges
The IT landscape combined many critical systems, including custom and legacy applications such as a home-grown HR system. The security team was small and responsible for many different parts of cybersecurity at once. A multi-year, multi-million IGA roll-out was simply not an option, and access reviews were still done with Excel exports and manual emails.
A hybrid, legacy-heavy IT landscape
Multiple critical systems, including custom applications and a home-grown HR system.
A small security team with a broad remit
A multi-year, multi-million IGA roll-out was not an option.
Access reviews on Excel and email
Manual, repetitive control tasks that took time and gave limited real control.
5 Tips On Achieving Mature Access Governance Within Days
Securing access to data and applications has become a cornerstone of any modern cybersecurity strategy.
- ✅ Why do Identity and Access Management (IAM) projects often fail?
- ✅ The Essentials of Mature User Access Management
- ✅ Tips How You Can Control User Access With Minimal Effort
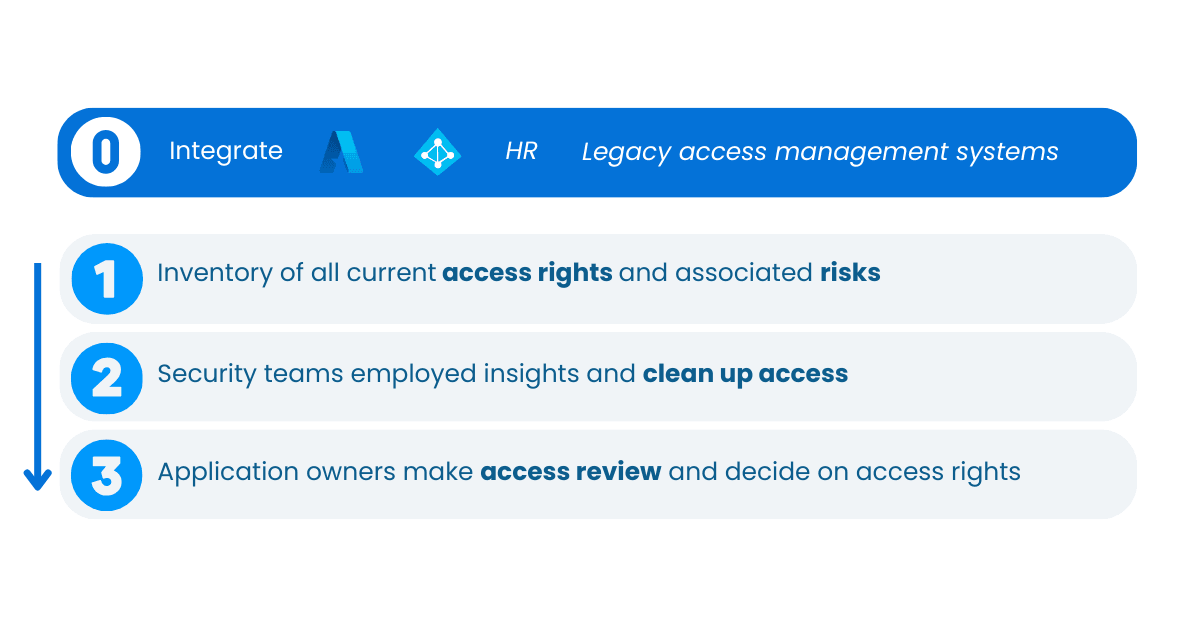
Key Results
Within days, the team could see every user and their access across all sources. That visibility made the risky accounts visible: five types of orphaned accounts, active accounts of external contractors who had already left, and users with excessive access rights. They were cleaned up, which also reduced licence costs.
The solution
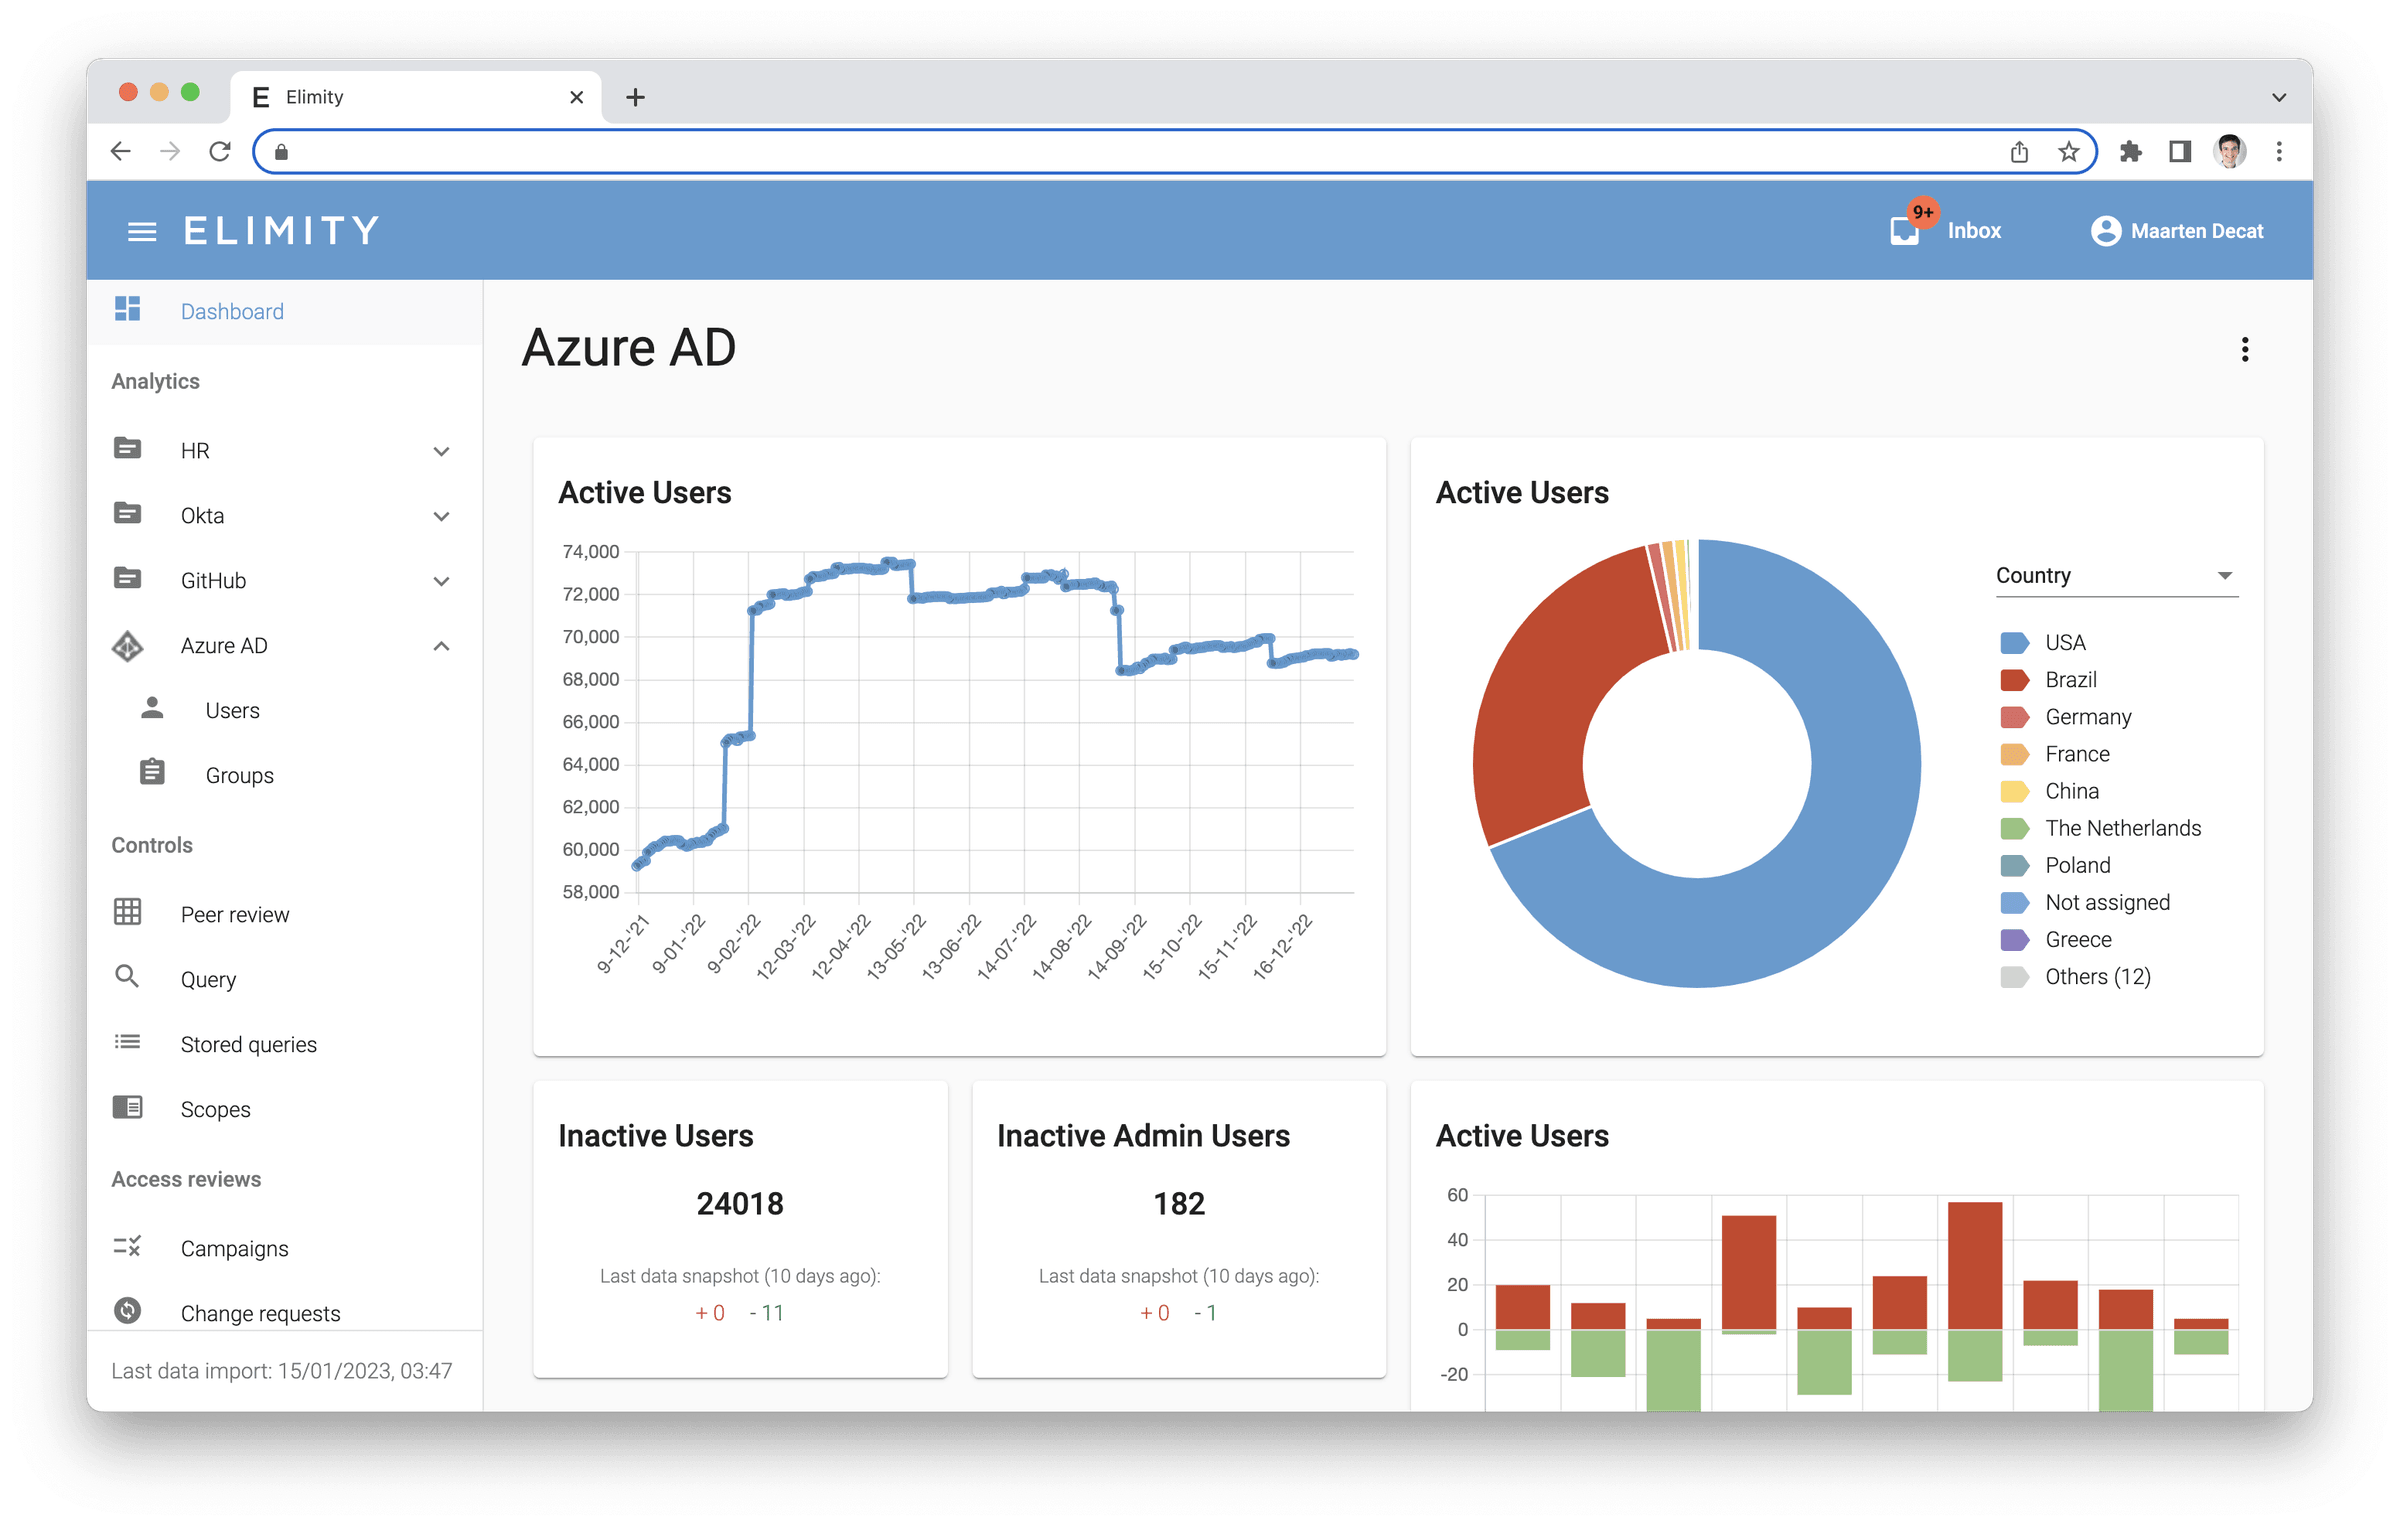
Fédérale Assurance deployed Elimity and connected 8 sources: two HR systems, Active Directory, Azure AD, Windows file shares and local admin accounts. Elimity linked all of this data into one up-to-date view. From that point on, the whole security team could work from the same facts instead of separate exports. The team could:
- Track essential security controls
- Ask the business for input through access reviews
- Clean up risky access
- Run their own identity analyses, one question at a time
The case in numbers
The project was built step by step, with results from the very first days. Here is what the first four months looked like.
- 2 daysFirst visibility of users and their access
- 2 weeks8 sources connected
- 1 month50 security controls and automated KPIs
- 2 months60 critical orphaned accounts removed
- 3 months70 access reviews sent out
- 4 months400+ change requests
Benefits
In the end, Fédérale Assurance got solid governance of users and access at around 1/20th of the cost of an IGA deployment. The security team became more productive, the business found access reviews easier to complete, and the company had the audit evidence it needed for ISO 27001.
KPI-Driven Approach to IAM
Our guide walks you through everything you need to start using KPIs to improve your IAM security.
Your Ultimate IGA-Deployment Checklist
Are you starting your identity governance and administration (IGA) journey? Follow Elimity's checklist for successful IGA deployment.
Applications in Scope
Eight identity sources were connected, covering both cloud and on-premises systems.